Now Reading: CERT-In warns of hacking risk in Tata connected car apps
-
01
CERT-In warns of hacking risk in Tata connected car apps

The Story in Brief
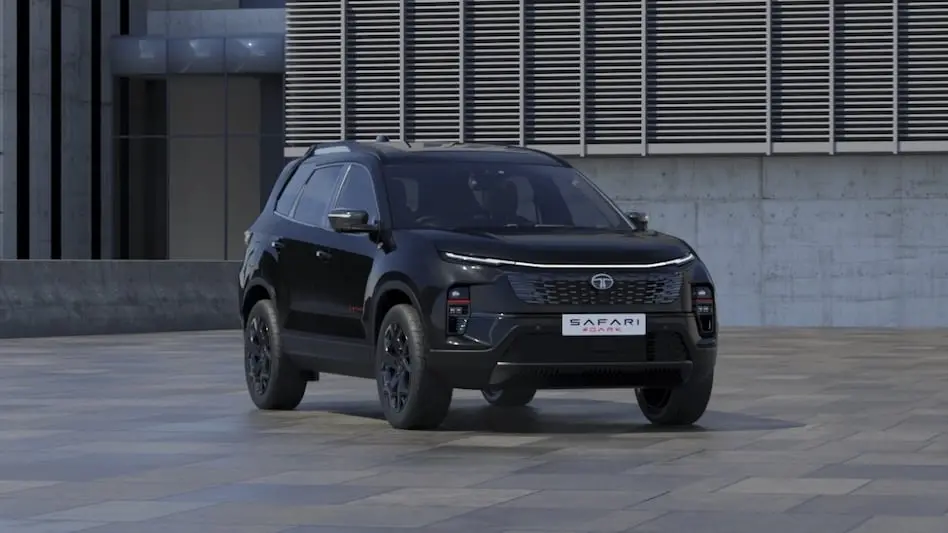
India's Computer Emergency Response Team (CERT-In) has issued a high-severity warning about security flaws in Tata Motors' connected vehicle apps iRA 2.0 and iRA.ev. The government agency said the vulnerabilities could allow hackers to access sensitive credentials, vehicle information and services, and even impersonate users or modify app data without permission.
CERT-In identified four security weaknesses in iRA 2.0 version 26.73 and below and iRA.ev version 26.72 and below. The app lets users remotely lock doors, track location and check vehicle health. The agency has advised all users to update their app software immediately.
Indian Opinion Analysis
Both Aaj Tak and Amar Ujala report the same CERT-In warning about security flaws in Tata Motors' iRA 2.0 and iRA.ev apps, with nearly identical facts on affected versions and risks. Aaj Tak leads with the government agency's warning and describes the hacker threat directly, while Amar Ujala leads with a user caution and lists four specific vulnerabilities. Neither outlet adds editorial commentary or attributes blame, both present the matter as a straight security advisory. The coverage is uniform straight reporting, differing only in presentation style. The concrete next step from both sources is for users to update their app software immediately.
Coverage: 2 sources, 2 neutral
Sources (2): aajtak.in (neutral report), amarujala.com (neutral report)
This brief was synthesised by AI from the 2 sources linked above, so one read covers every framing they carry. Methodology and corrections.