Now Reading: Eight weak eMudhra certificate keys trigger global browser blocks
-
01
Eight weak eMudhra certificate keys trigger global browser blocks

The Story in Brief
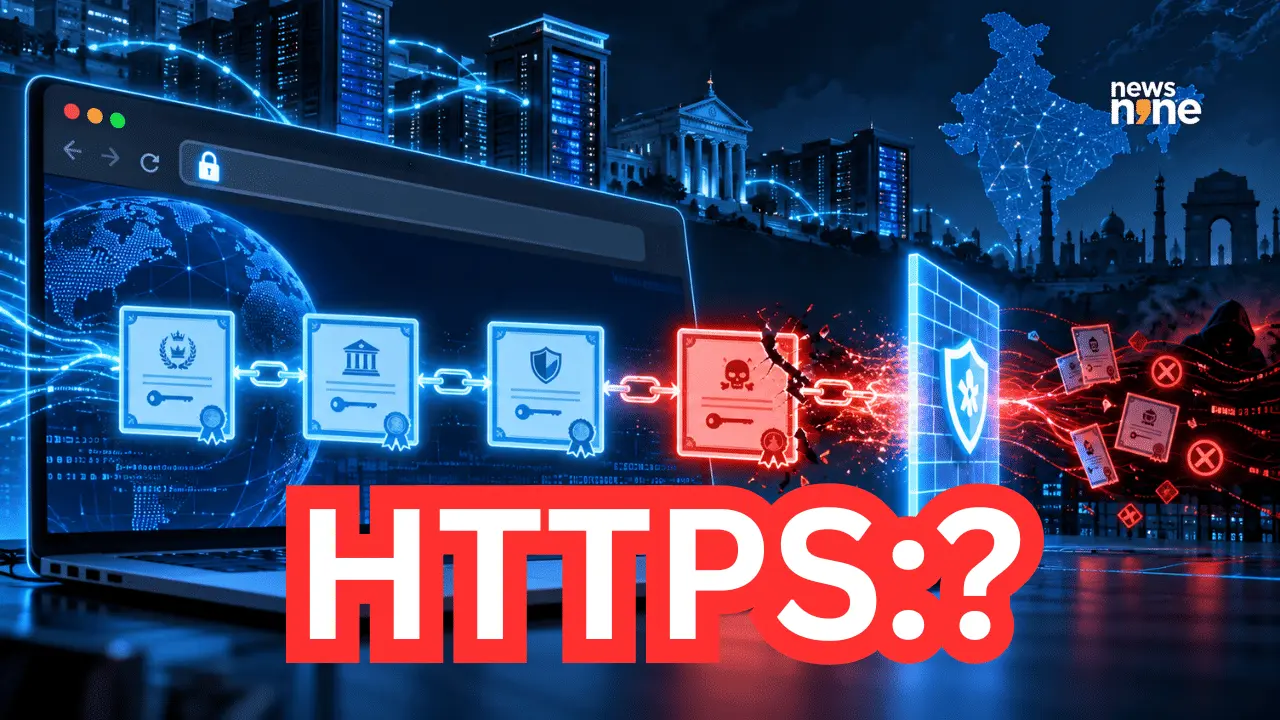
Eight intermediate certificate authority keys issued by Bengaluru-based eMudhra were generated with weak values, including the number 4, letting anyone recover them in seconds, prompting Google, Apple, Microsoft and Mozilla to block the affected certificates between October 17 and October 20. Mozilla, which first published an incident report, called the impact ‘could not be higher’. The flaw arose from a script error during a key generation ceremony in April 2025, eMudhra said, and went unnoticed for 18 months until a researcher named Wayne reported it. No data breach occurred, no end-entity certificates were issued through the weak keys, and eMudhra’s Indian digital signature and eSign services are unaffected, the company said.
The affected global TLS business accounts for about 1% of eMudhra’s revenue. Shares fell 20% on Wednesday to ₹432. eMudhra is working directly with potentially affected customers to issue replacement certificates and is continuing its root-cause investigation.
Update, 21 October 2026: New reports from Business Standard, Digit and Hindustan Times confirm that one key was just the number 4, and that the certificates were blocked by Google and Mozilla on October 17, Apple on October 19 and Microsoft on October 20. Mozilla also announced an emergency removal of trust in one of eMudhra’s root certificates on October 20, and eMudhra said about 30,000 customers’ certificates now need reissue. The company’s investigation remains open.
Indian Opinion Analysis
All six outlets report the same core facts: eight weak eMudhra certificate keys were generated in April 2025, discovered on October 17, and blocked by Google, Apple, Microsoft and Mozilla. Business Standard and Digit add technical detail, one key was just four, that Hindustan Times leads with for drama, while CNBC-TV18 and Business Line focus on the stock drop and eMudhra’s reassurance that only 1% of revenue is affected. Times Now strikes a sensationalist tone with ‘risks about fake websites’ and a minor error (‘private jets’ instead of ‘private keys’). Every source confirms no data breach and no malicious use found. The uniform straight reporting leaves the story’s open question, whether eMudhra’s investigation will find any exploited certificates, as the concrete watch item.
Coverage: 6 sources, 5 neutral, 1 sensationalist
Sources (6): cnbctv18.com (neutral report), thehindubusinessline.com (neutral report), timesnownews.com (sensationalist), business-standard.com (neutral report), digit.in (neutral report), hindustantimes.com (neutral report)
This brief was synthesised by AI from the 6 sources linked above, so one read covers every framing they carry. Methodology and corrections.